
CMMC compliance consultant
CMMC Level 2.Ready to defend.
A CMMC compliance consultant scopes the systems that touch CUI, scores all 110 Level 2 requirements against how you work, and runs the readiness review before a C3PAO does.
- NIST 800-171 mapped
- POA&M with owners
- Not a C3PAO
Your contract and the prime flow-down say which level applies
The readiness work
How the engagement runs
- 01
Scoping & gap analysis
Define the assessment boundary — which systems touch CUI — and score all 110 NIST 800-171 requirements against current practice.
- 02
SSP & POA&M build
Write the System Security Plan and build a POA&M with owners, dates, and milestones.
- 03
Remediation sprint
Close the gaps that move the score: MFA, encryption, logging, and access reviews, sequenced by risk and effort.
- 04
Mock assessment
A readiness review with evidence testing, then a score against the requirements and a go or no-go recommendation.
The supply chain
From the shop floor to a score you can post
Before
Patching happens and access comes off when someone leaves, but the SSP is thin and the POA&M is stale. An assessor cannot score what is not written down.
After
The boundary names the systems that actually touch CUI. The POA&M has owners and dates. The team answers from the work, and the score in SPRS is one they can stand behind.
Policy, procedure, evidence
The program stands on all three
Policy is the System Security Plan that matches the real boundary. Procedure is the POA&M: owners, dates, and the order the gaps close.
Evidence is what the readiness review tests — document review, then interviews, then the controls themselves. 5-point items, and anything involving MFA, encryption, or boundary protection, have to be closed.
Evidence
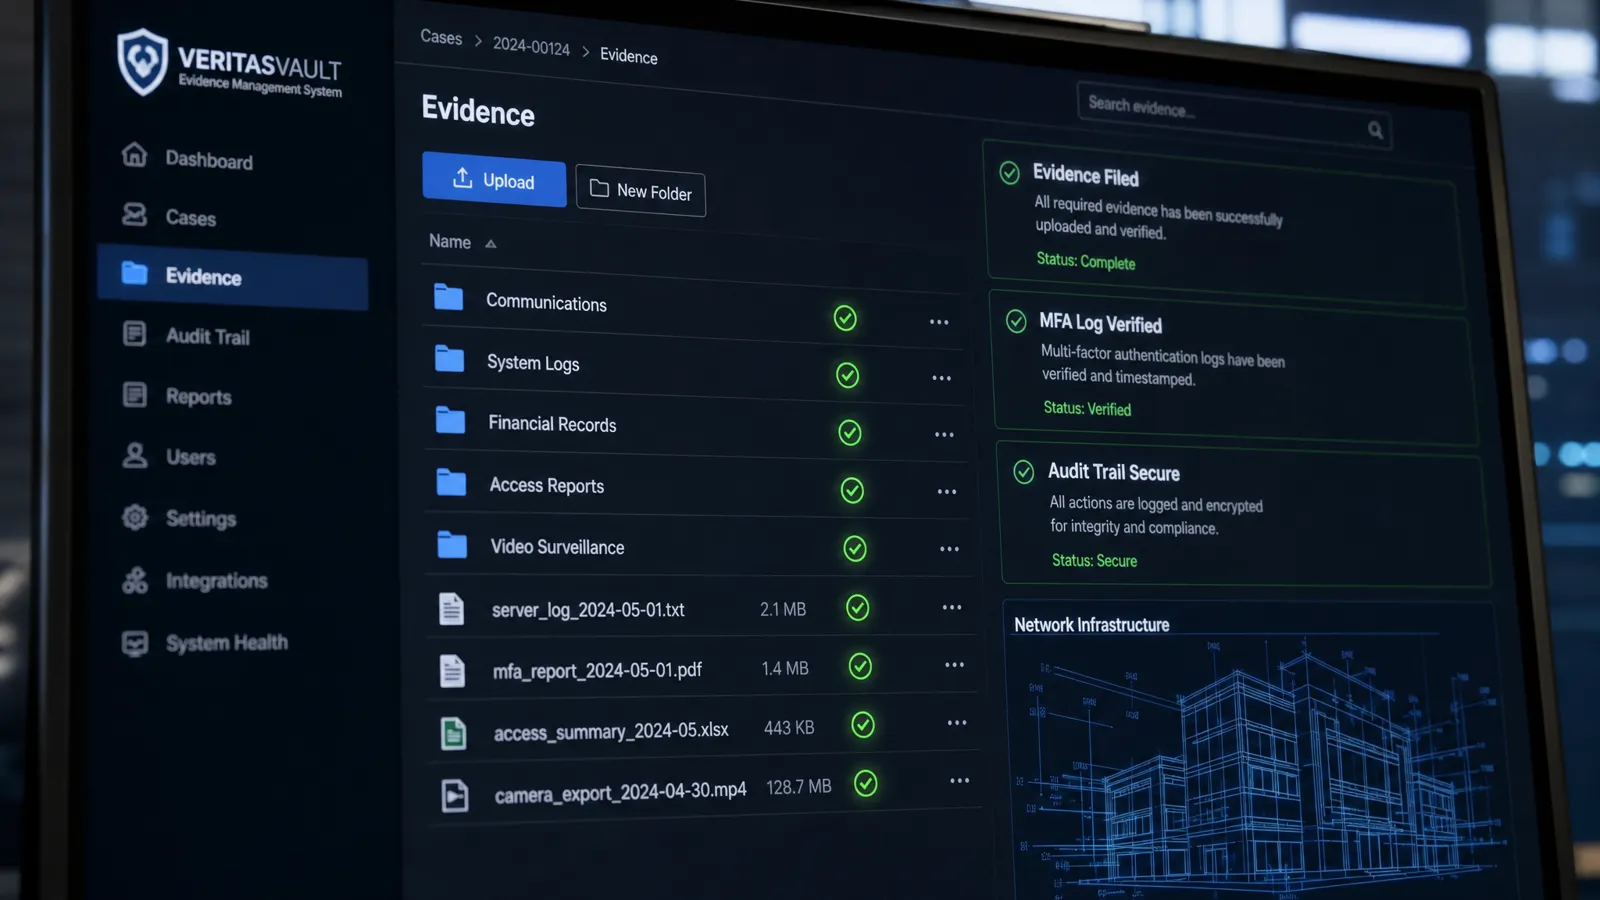
Artifacts an assessor can test
The usual stall is evidence. The controls exist in practice. They are not written in a way the assessment can score.
The screen is an illustration of that library: logs, access reports, MFA records. What you leave with is the SSP, the POA&M, and a score against the requirements.
Orange County
Home base on the coast
GRYHAT is based in Mission Viejo. Orange County and California are the local work, on the same line as everyone else: (714) 794-2803.
The readiness check is the same wherever the contract sits. CUI, the contract or award date, and company size decide the boundary and whether Level 1 or Level 2 is the real target.
What GRYHAT is
Level 1. Working toward Level 2. Not the assessor.
GRYHAT is CMMC Level 1 and is working toward Level 2. We run CMMC Level 2 readiness assessments and guide companies to Level 2. A provider does not need its own Level 2 certification to do that work.
GRYHAT is not a certifying assessor and does not issue CMMC certification. Certification is issued by a C3PAO. The readiness work is document review, interviews, and testing, done before that assessment.
Entry offer
CMMC Level 2 readiness check
Three questions, then a time on the calendar or a note to Andy V. We use them to see whether CMMC Level 2 applies and how close the contract date is.
GRYHAT is CMMC Level 1 and is working toward Level 2. This readiness check scopes your Level 2 path and the evidence you already have. We run CMMC Level 2 readiness assessments and guide companies to Level 2. A provider does not need its own Level 2 certification to do that. GRYHAT is not a certifying assessor and does not issue CMMC certification.
Andy V · eva@gryhat.com
Questions
Straight answers
We scope the CUI boundary, score the NIST SP 800-171 requirements, write the System Security Plan and POA&M, close the gaps that move the score, and run a CMMC Level 2 readiness assessment. GRYHAT is CMMC Level 1 and is working toward Level 2. We guide companies to Level 2. A provider does not need its own Level 2 certification to do that. GRYHAT is not a certifying assessor and does not issue CMMC certification.
CMMC Level 2 is the full NIST SP 800-171 set: 110 requirements for contractors that store, process, or transmit CUI. Level 1 is 15 basic safeguarding requirements and applies when you only handle Federal Contract Information. Your contract and prime flow-downs say which one you are in.
If you store, process, or transmit CUI and hold or want DoD contracts, CMMC requirements phase in between 2025 and 2028 depending on contract value and level. Self-assessment obligations already apply to many contracts, and primes commonly require scores before the regulation formally demands them.
SPRS (Supplier Performance Risk System) is the DoD registry where contractors post their NIST 800-171 self-assessment scores, from 110 down based on findings. Contracting officers and primes check it during award decisions. An unposted score is visible as a gap.
Level 1 (15 requirements) applies when you only handle Federal Contract Information. Level 2 (110 requirements, full NIST 800-171) applies when you handle CUI. Your contracts and prime flow-downs tell you which. The readiness check starts by reading them with you.
Yes. A limited number of 1-point and 3-point requirements can remain open on a POA&M with a closed date. 5-point items, and anything involving MFA, encryption, or boundary protection, have to be closed. We sequence remediation so POA&M items are genuinely temporary.
It depends on current practice and how clean the CUI boundary is. Starting before a contract demands the work leaves more room to sequence it.
24/7 · (714) 794-2803
Book the readiness check.
Three questions — CUI, the contract date, and company size — then a time on the calendar. Or call the 24/7 line and email eva@gryhat.com.